The problem
Automated creative generation needed subscription-aware usage controls rather than an unlimited public webhook.
My responsibility
Built validation, Airtable tracking, generation, upload, status, and usage-update stages.
Evidence
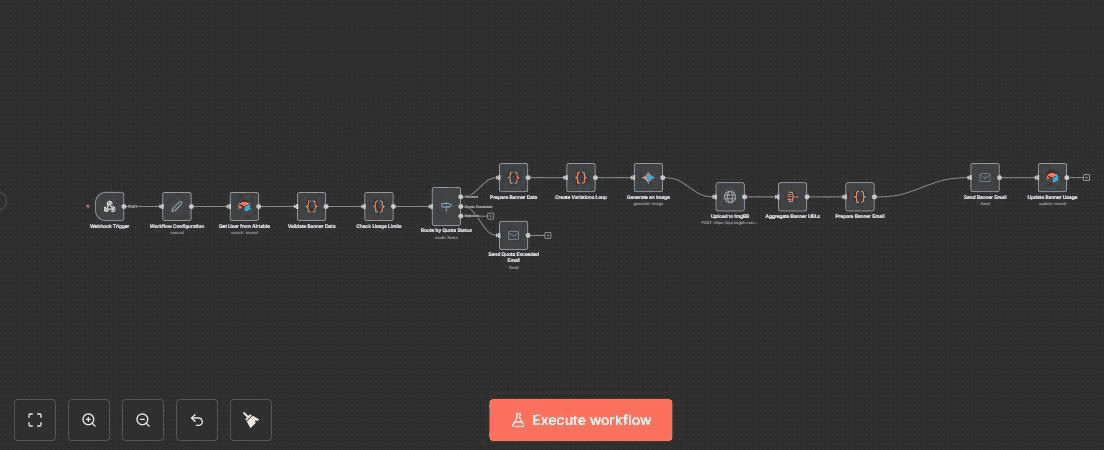
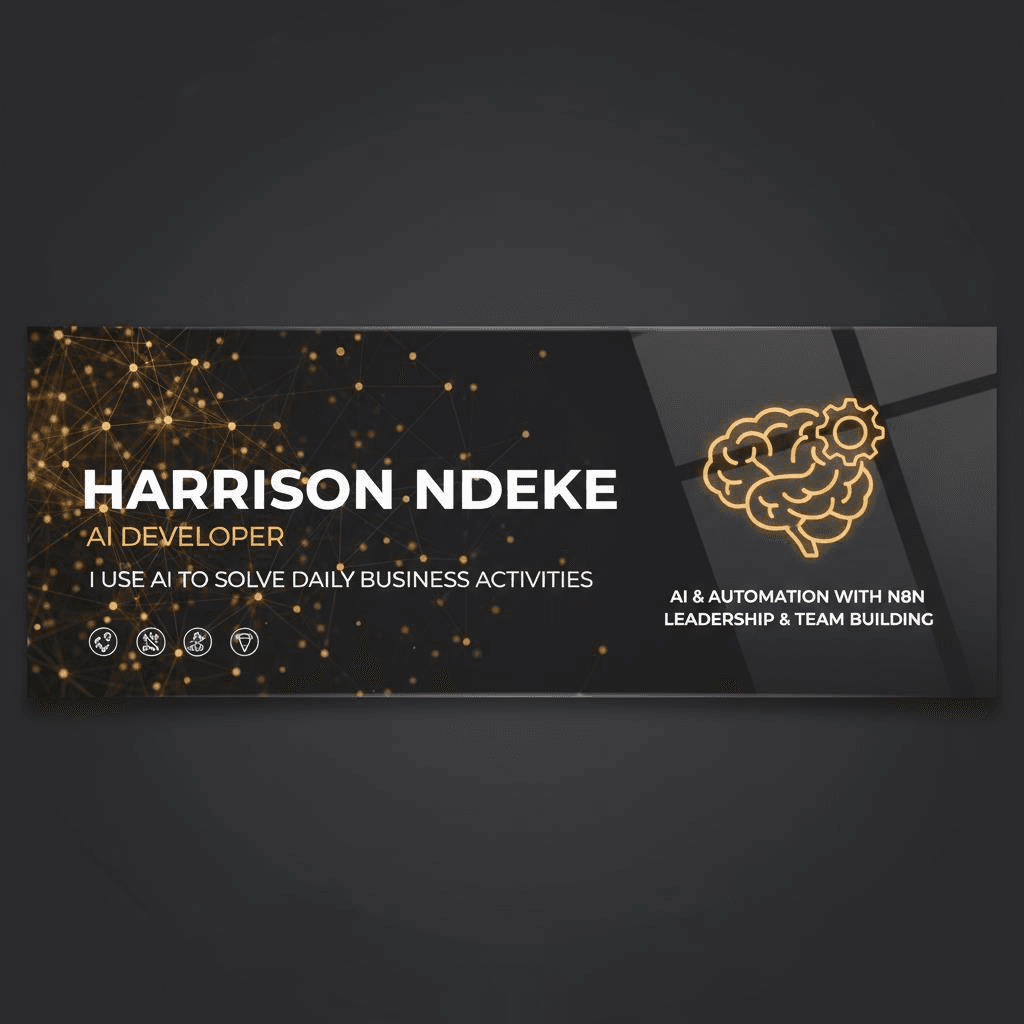
Screenshots from the live system and the workflow itself — captions describe only what is visible.
System route
The architecture below is a readable abstraction of the documented workflow, not a simulated live execution.
- Validate request
- Check account and usage
- Generate and upload banner
- Update entitlement record
Reliability notes
- Usage is checked before generation.
- Entitlement and status records update after execution.
Operational Architecture & Deep Dive
In production automation, reliability is never an afterthought. Every mission engineered for LinkedIn Banner Generation Pipeline is designed around strict input validation contracts, bounded execution permissions, and deterministic error fallback channels. Unstructured data is parsed into schema-validated JSON before entering downstream business logic, preventing malformed payloads from corrupting state stores or generating cascading failures.
When integrating large language models with operational databases and third-party APIs (n8n, Airtable, Gemini), workflows utilize prompt-injection filtering, deterministic routing, and transactional rollback mechanisms. Rather than treating failures as exceptions, the architecture explicitly models failure as a first-class execution path with automated retry policies and real-time alerting.
Evidence currently available
- Full pipeline screenshot
Technology used
Zero-Trust Governance & HarLyn Security Standards
Through HarLyn Digital Partners, all automated systems undergo zero-trust threat modeling, OWASP Top 10 vulnerability checks, and Kenya Data Protection Act (KDPA) compliance reviews led by CompTIA Security+ certified assurance engineers. API keys are vaulted with strict least-privilege scoping, preventing unauthorized data exfiltration or unmonitored external tool execution.
Evidence Verification & Authorized Review
Client-approved execution recordings, live production endpoints, sanitized payload schemas, and verifiable metric baselines are documented across HarLyn Digital Partners repositories. Teams seeking an in-depth operational audit can explore our fixed-fee 48-Hour Secure Digital Workflow Assessment.