The problem
Customers wanted a way to own a smartphone (Samsung, Tecno, Infinix, Redmi) without the barrier of the full retail price up front, while the business needed a reliable way to manage active devices and customer accounts at scale.
My responsibility
Built the customer-facing application and the internal fleet-management admin dashboard used to run the business day to day. Internal device-security architecture is proprietary to the business and is not detailed publicly.
Evidence
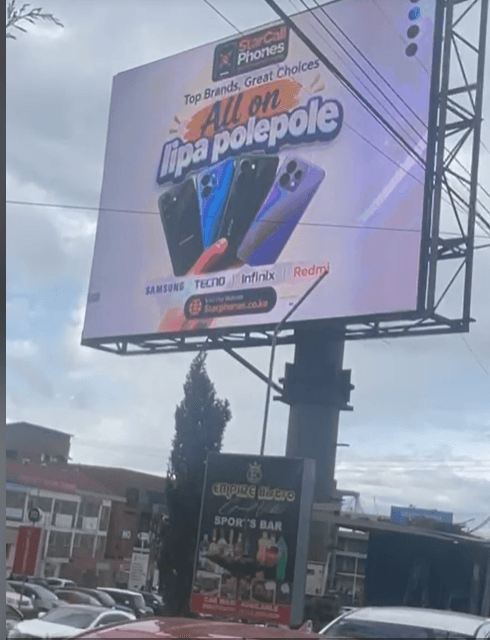
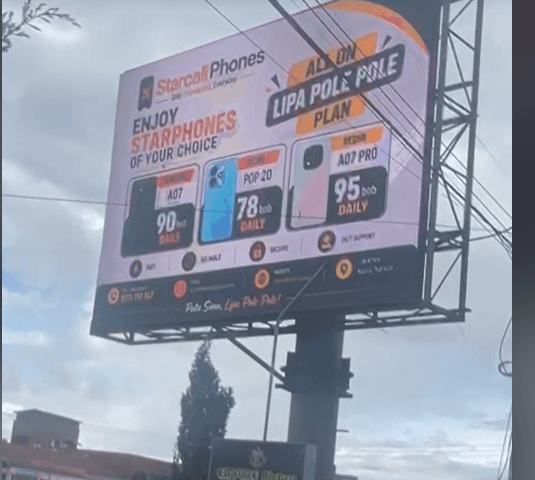
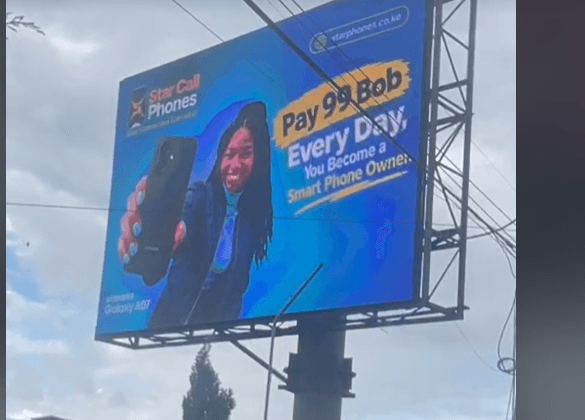
Screenshots from the live system and the workflow itself — captions describe only what is visible.
System route
The architecture below is a readable abstraction of the documented workflow, not a simulated live execution.
- Customer selects a device and a daily payment plan
- Device and customer account are registered to the platform
- Admin dashboard tracks the active device fleet and payment status
- Customer completes daily instalments toward full ownership
Reliability notes
- Public claims are limited to what is visible in the company's own advertising and public presence.
- Internal architecture, device-security design, and backend infrastructure are intentionally not published — this is production security tooling for a live business.
Operational Architecture & Deep Dive
In production automation, reliability is never an afterthought. Every mission engineered for StarCall Phones — Device Financing Platform is designed around strict input validation contracts, bounded execution permissions, and deterministic error fallback channels. Unstructured data is parsed into schema-validated JSON before entering downstream business logic, preventing malformed payloads from corrupting state stores or generating cascading failures.
When integrating large language models with operational databases and third-party APIs (Native Android Development, Next.js Admin Dashboard), workflows utilize prompt-injection filtering, deterministic routing, and transactional rollback mechanisms. Rather than treating failures as exceptions, the architecture explicitly models failure as a first-class execution path with automated retry policies and real-time alerting.
Evidence currently available
- City billboard advertising campaign
- Live company website
Technology used
Zero-Trust Governance & HarLyn Security Standards
Through HarLyn Digital Partners, we review automated systems for security risks using threat modeling, OWASP-aligned checks, and technical data protection site audits led by Nazline Mwita. We store API keys in secure vaults and limit their permissions to reduce exposure.
Evidence Verification & Authorized Review
Client-approved execution recordings, live production endpoints, sanitized payload schemas, and verifiable metric baselines are documented across HarLyn Digital Partners repositories. Teams seeking an in-depth operational audit can explore our fixed-fee 48-Hour Secure Digital Workflow Assessment.